Software Engineering · Bengaluru
Zero Trust Security — in Bengaluru.
Never trust, always verify — security architecture for a perimeter-less world.
4.9/5 client rating
5.0 on Google
NDA-first, IP stays yours
Quote in 24 hours
Lower than you fear
First delivery
6–10 weeks
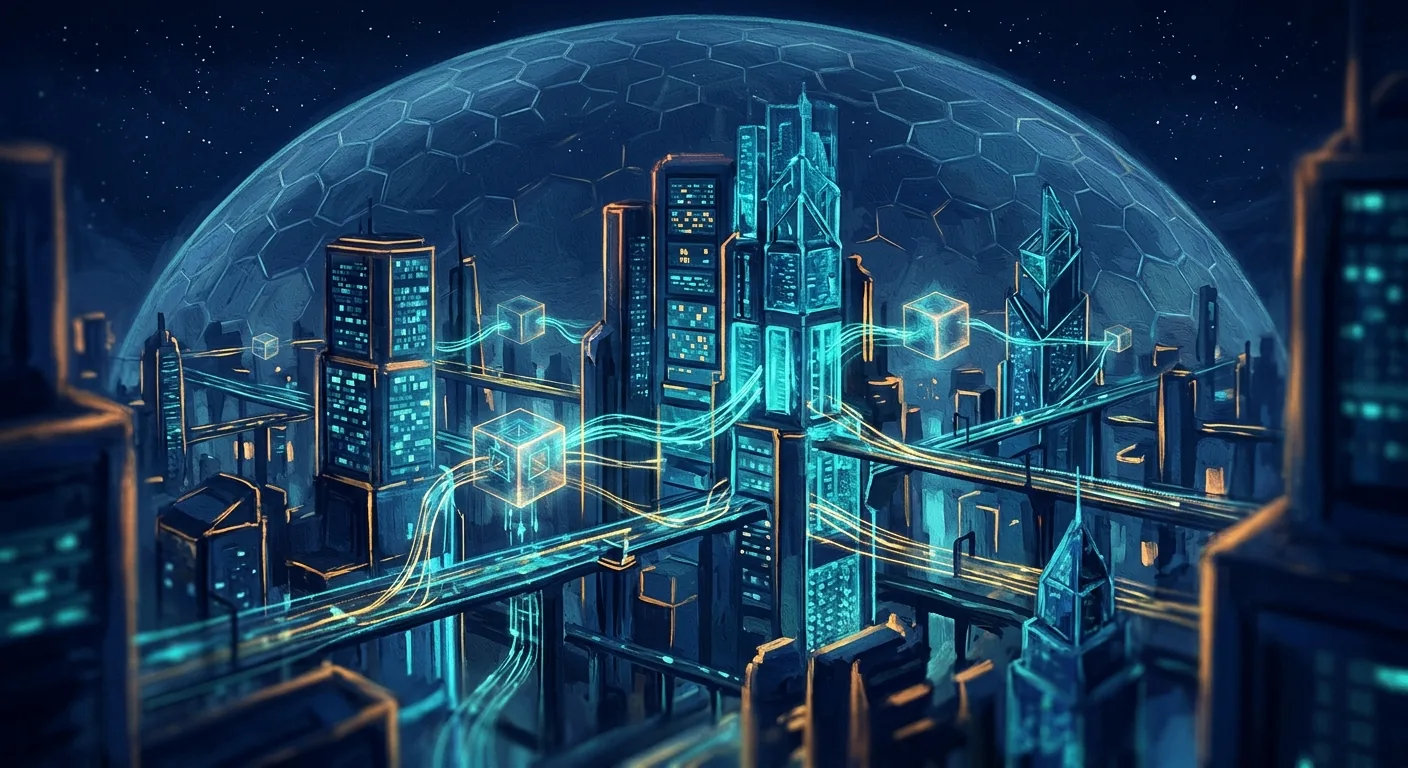
VERIFY EVERY REQUEST
Zero Trust for Bengaluru's distributed teams
With hybrid staff commuting on Namma Metro and vendors logging in remotely, network location proves little. We design continuous verification across users, devices, and workloads.
In plain terms
What Zero Trust Security actually gets you.
What it is
No one gets automatic access; every person and device must prove they should be let in.
What you get
You get tighter access rules so only the right people reach the right information.
Why it's worth it
That lowers the chance of leaks, fraud, and mistakes turning into serious business problems.
The Bengaluru reality
Perimeter thinking no longer protects access
Bengaluru companies no longer work behind one office firewall; people log in from Namma Metro commutes, client sites and home networks. With contractors, vendors and fast team changes, broad access rights become a real business risk.
The cost of waiting
Old trust models leak risk daily
If access is trusted by network location alone, one compromised device or account can move too far, too fast. For Bengaluru teams using SaaS, cloud, and contractors, that risk compounds every day.
The flip side
Tighter access control
Users get only the access they need, reducing risk from overshared tools and stale permissions.
The flip side
Safer hybrid work
Protect systems even when employees connect from homes, cafés or client locations across the city.
The flip side
Cleaner joiner exits
Access can be granted and removed with more discipline as teams scale or contractors rotate.
How we deliver in Bengaluru
Our answer, built for zero trust security here.
JSXDOM designs zero trust around identity, device posture and least-privilege access, not outdated network assumptions. We help you verify every user and system request so access stays tight even in hybrid, fast-moving teams.
What you get
Access controls mapped clearly
No vague promises. Your quote lists exactly what lands in your hands, and each one is explained in plain words.
Zero Trust assessment & roadmap
Current posture mapped against Zero Trust maturity — with a phased path, not a revolution.
Identity-first architecture
Strong identity as the new perimeter — SSO, MFA and conditional access everywhere.
Device trust & management
Only known, healthy devices touch your resources.
Micro-segmentation
Networks divided so one compromise can't become a company-wide breach.
Least-privilege access
Permissions right-sized and time-boxed — standing access eliminated.
Continuous monitoring & analytics
Behavior watched for anomalies across identity, device and network signals.
The gap we close
Beyond VPN-and-pray security
Identity-led access design
We structure access around user, device, and workload verification rather than broad internal network trust.
Policy mapping by workflow
We align controls to real employee, vendor, and service workflows so security rules remain usable in practice.
Practical rollout sequencing
We phase Zero Trust adoption to reduce disruption instead of forcing a risky all-at-once security overhaul.
What changes
What verified access enables
Tighter access control
Users get only the access they need, reducing risk from overshared tools and stale permissions.
Safer hybrid work
Protect systems even when employees connect from homes, cafés or client locations across the city.
Cleaner joiner exits
Access can be granted and removed with more discipline as teams scale or contractors rotate.
Who we build for
Best fit for these teams right here in Bengaluru.
Whatever stage you're at in Bengaluru — first site or full rebuild — this is shaped around you.
Distributed companies
A perimeter-less workforce with perimeter-grade security.
Regulated industries
Controls that satisfy auditors by architecture, not paperwork.
Teams after lateral-movement scares
Segmentation so the next phished credential goes nowhere.
The studio in motion
Imagination, on loop.
Every frame below is original JSXDOM concept art — the same creative engine we point at your product.
Delivered the Bengaluru way
Local where it matters.
Full IST overlap
Standups in your morning, demos by your evening. On-site kickoff in Bengaluru for larger builds.
INR invoicing, GST-ready
Indian tax documentation as standard. Fixed written quote before we start — never hourly fog.
NDA-first, always
Your idea is protected before you share it — and your IP is assigned to you from day one.
First delivery in week one
Something real in your hands inside the first week — momentum from day one, not month three.
Proof, not promises
Why execution stays practical
You can judge our Zero Trust work by the policy model: identities, device posture, service access, and least-privilege rules mapped to real workflows. Our team tests exceptions, session controls, and break-glass paths so security does not cripple operations.
Fixed written quote
Scope, milestones and price in writing before a rupee moves.
NDA before details
Your idea stays protected from the very first conversation.
Senior pod, named
You know exactly who builds — no junior hand-offs.
IP stays yours
Code, designs and docs assigned to you on final payment.
Zero Trust
Your perimeter died with the office. Your security didn't get the memo.
Never trust, always verify — architecture for a world where the network is everywhere.
Asked in Bengaluru
Zero Trust FAQs
Not if you have hybrid work, SaaS sprawl or customer security requirements. It’s often a practical fix for messy access, not just a big-company project.
Get started
Book a free consultation.
30 minutes with a senior expert — we map the route together, whatever you're building.